

Prerequisites
Before you begin, ensure you have:- Administrator access to your Microsoft Entra ID tenant
- A Brellium account with the can edit sso settings permission, with SSO and SCIM turned on for your organization (see Access the Brellium setup portal)
Access the Brellium setup portal
IT administrators can open the SSO and SCIM setup portal on their own. In Brellium, go to Control Center > Settings. The Single sign-on and Directory sync (SCIM) sections each have an Edit configuration button. Each button opens the setup portal for that connection in a new tab, so you can configure and change settings without a support ticket.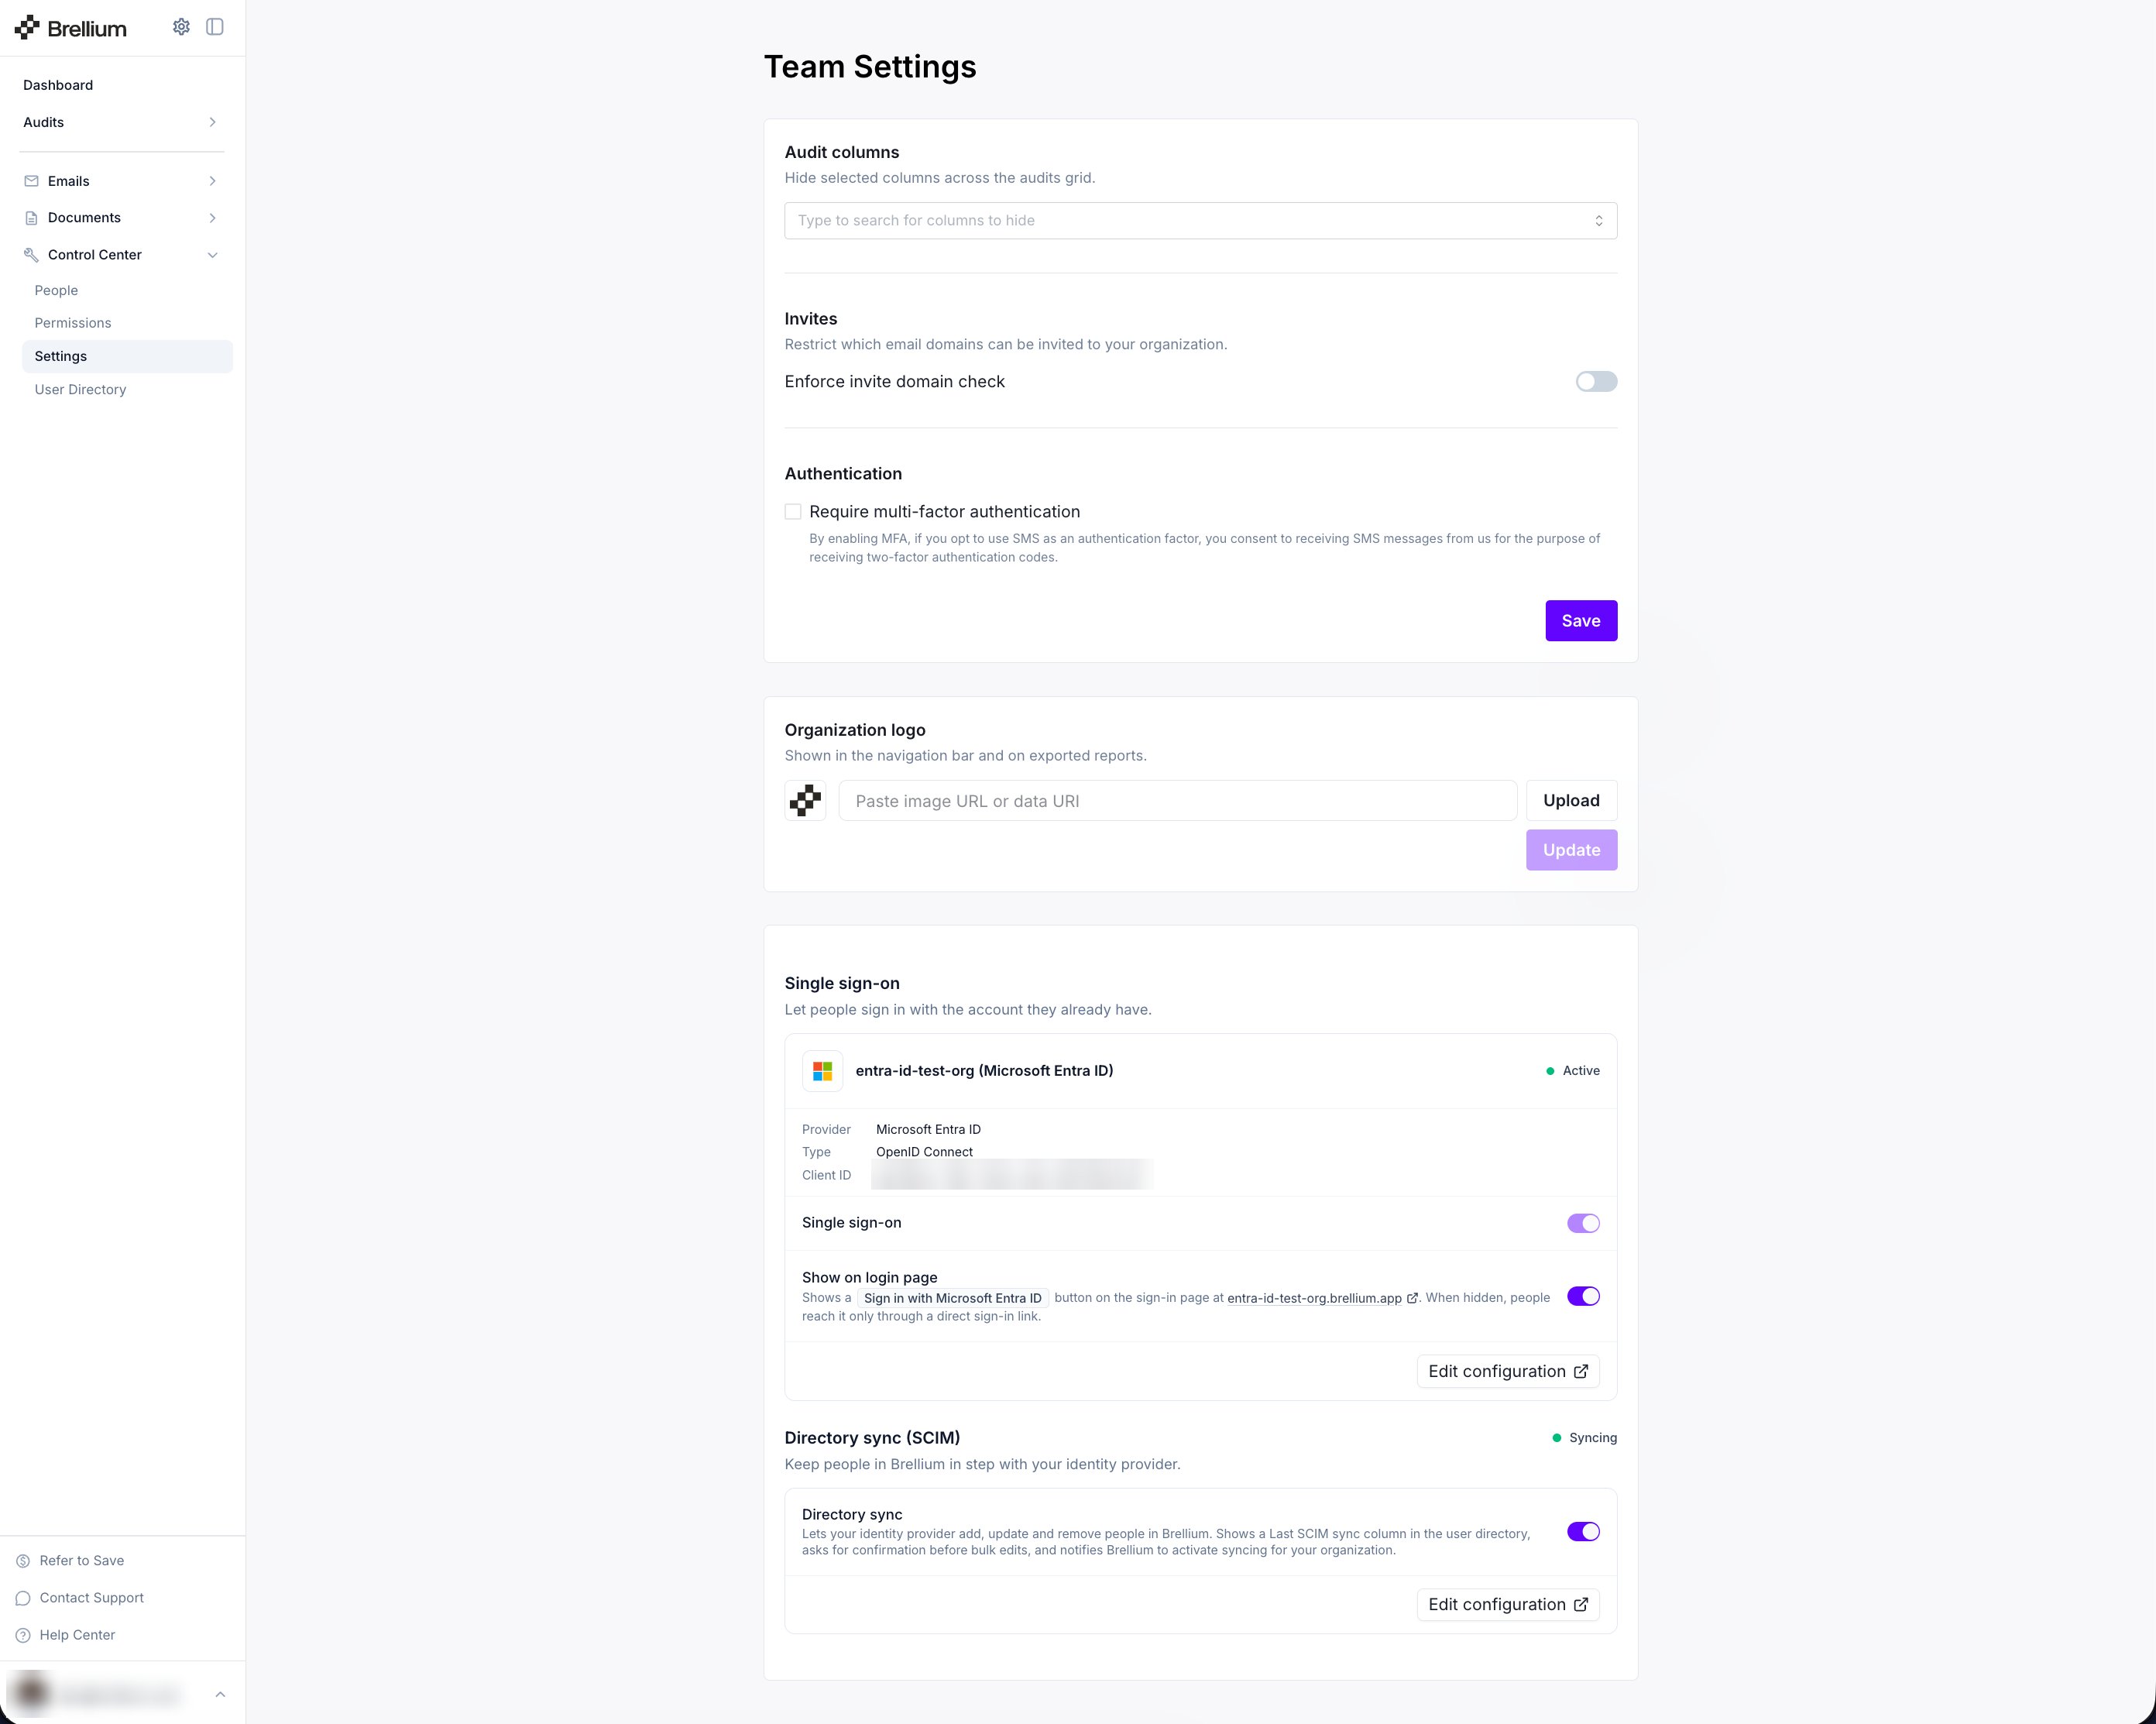
Brellium Control Center > Settings — the Single sign-on and Directory sync (SCIM) sections
- SSO and SCIM are turned on for your organization. If you do not see the Single sign-on and Directory sync (SCIM) sections on the settings page, contact your customer success manager to turn on the feature for your organization. You can open the SSO and SCIM configuration only after the feature is on.
- You have the can edit sso settings permission. Your Brellium account must have the can edit sso settings permission under Settings. The can edit org settings permission does not give access to SSO and SCIM. If you do not have the permission, ask a Brellium administrator in your organization to give it to you.
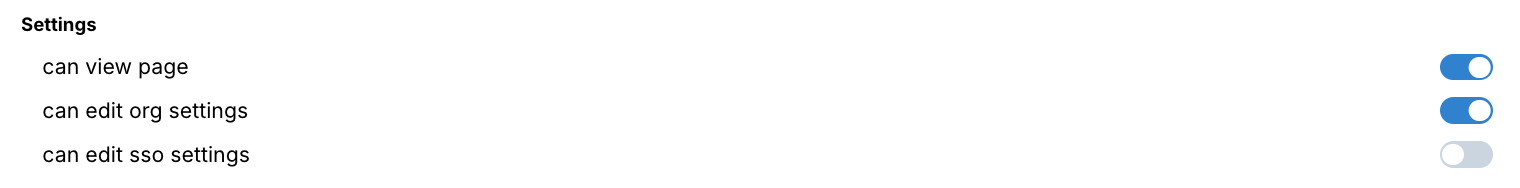
The can edit sso settings permission under Settings
Supported features
The Brellium Microsoft Entra ID integration supports the following features:- SP-initiated SSO — Users can sign in to Brellium from the Brellium sign-in page, which redirects to Microsoft Entra ID for authentication.
- IdP-initiated SSO — Users can sign in to Brellium directly from the Microsoft My Apps portal by clicking the Brellium tile.
- Just-In-Time (JIT) provisioning — User accounts are automatically created in Brellium on first sign-in through Microsoft Entra ID. The following attributes are provisioned:
- Email address
- Full name
- Federated logout (SLO) — Users who sign out from Brellium also have their Microsoft Entra ID session terminated.
To provision and deprovision users in Brellium using SCIM, see the SCIM Provisioning Configuration guide.
Configuration steps
1
Register an application in Microsoft Entra ID
- Sign in to the Microsoft Entra admin center.
- Go to Identity > Applications > App registrations.
- Click New registration.

App registrations page with New registration button
- Configure the following settings:

Register an application form
- Click Register.

Application overview showing the Application (client) ID
- In the registered Brellium application, go to Authentication under Manage.
- Click Add a platform and select Web.

Add a platform — select Web
- Enter the Redirect URI from the Brellium setup portal.
- Click Configure.

Configure Web platform with Redirect URI
2
Create a client secret
- In the registered Brellium application, go to Certificates & secrets under Manage.
- Click New client secret.
- Enter a description (e.g.,
Brellium SSO) and select an expiration period.

Add a client secret dialog
- Click Add.
- Copy the Value of the new client secret immediately — it is only shown once.

Client secret value — copy this immediately
3
Add API permissions
- In the registered Brellium application, go to API permissions under Manage.
- Click Add a permission > Microsoft Graph > Delegated permissions.
- Add the following permissions:
- Click Add permissions.
- If required by your organization, click Grant admin consent to consent on behalf of all users in the directory.
4
Enter the credentials in the Brellium setup portal
- In Brellium, go to Control Center > Settings.
- Under Single sign-on, click Edit configuration. The setup portal opens in a new tab.
- Enter the following values to complete the connection:
If you cannot open the setup portal, see Access the Brellium setup portal.
5
Grant admin consent
The setup portal asks an administrator in your Azure AD tenant to grant consent for the application.
- When the setup portal prompts you, sign in with an Azure AD administrator account.
- Review the permissions and click Accept.
If you do not have the Azure AD administrative permissions to grant consent, ask an administrator in your organization to complete this step in the setup portal.
6
Assign users and groups
- In the Microsoft Entra admin center, go to Identity > Applications > Enterprise applications.
- Select the Brellium application.
- Go to Users and groups under Manage.
- Click Add user/group.
- Select the users or groups to assign and click Assign.
7
Verify the configuration
Verify that SSO is working correctly.Verify IdP-initiated SSO:
- Go to the Microsoft My Apps portal.
- Click the Brellium tile.
- Confirm that you are signed in to Brellium without being prompted for additional credentials.
- Open a new browser window and go to the Brellium sign-in page.
- Click Sign in with Microsoft.
- Enter your Microsoft Entra ID credentials.
- Confirm that you are signed in to Brellium.
SP-initiated SSO
After the integration is configured, users can sign in to Brellium using one of the following methods:For SP-initiated SSO, users must access Brellium through one of the options below. Direct sign-in at
app.brellium.com without a verified domain will not automatically redirect to Microsoft Entra ID.https://myorganization.brellium.app). You are automatically redirected to Microsoft Entra ID for authentication.
Option 2: Sign in with a verified domain
If your organization has configured verified domains:
- Go to https://app.brellium.com.
- Enter your email address.
- You are automatically redirected to Microsoft Entra ID for authentication based on your email domain.
Troubleshoot
Signing key rollover
Microsoft Entra ID periodically rolls its signing keys for security purposes. You do not need to take any action — Brellium uses the new key automatically.Support
If you have questions or encounter issues not covered in this guide, contact the Brellium support team:- Email: sso.support@brellium.com